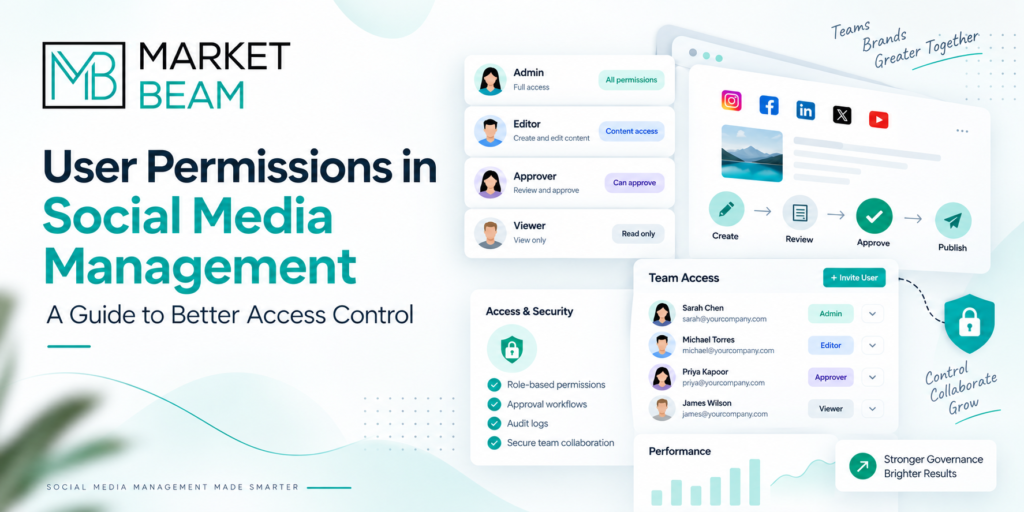
User permissions are becoming essential for enterprise social media management. As more employees, agencies, reviewers, publishers, and regional teams work across the same social media environment, organizations need better control over who can create, review, publish, analyze, and manage content.
Giving every user the same level of access creates unnecessary risk.
For example, a content creator may need to draft posts but not publish them. A reviewer may need to approve content without accessing system settings. Similarly, an analytics user may need performance data without having permission to modify or publish social media content.
Granular user permissions solve this problem by giving each person access based on their actual responsibilities.
For enterprise organizations, especially those operating in regulated industries, this approach can strengthen social media governance, improve permission management, reduce publishing risk, and create clearer content approval workflows.
What Are User Permissions?
User permissions define what an individual is authorized to access or do within a software platform.
In social media management, permissions can determine who can:
- Create social media content
- Review content
- Publish and schedule posts
- Manage users
- View analytics
- Monitor social media activity
- Access audit functionality
- Change platform settings
The principle is straightforward:
Give users the access they need to perform their responsibilities without automatically giving them access to everything else.
This becomes increasingly important as organizations manage more employees, brands, agencies, social accounts, and regional teams.
Why Are User Permissions Important for Social Media?
Enterprise social media rarely involves a single person.
A social media post may move between a content strategist, designer, product marketer, reviewer, social media manager, regional team, and final publisher before it goes live.
Without clearly defined user permissions, these responsibilities can overlap.
For example, someone who only needs analytics could accidentally receive publishing access. A content creator could modify content that has already been scheduled. Likewise, a contractor could receive administrative privileges that are unnecessary for their work.
Granular permissions establish clearer boundaries.
Instead of asking:
“Does this person have access to our social media platform?”
organizations should ask:
“What should this person be allowed to do?”
That distinction is fundamental to effective permission management.
User Permissions vs. Traditional Admin Roles
Many software platforms traditionally rely on broad roles such as Administrator, Manager, Editor, and User.
While simple, these roles can become restrictive for complex organizations.
An administrator role, for instance, may combine publishing, analytics, user management, and settings access. However, someone responsible for managing users may not need publishing authority.
Granular user permissions separate these capabilities.
| Traditional Access | Granular User Permissions |
| Broad Admin roles | Individual capabilities |
| Similar access across the organization | Access can vary by team |
| Administrative functions bundled together | Functions can be separated |
| Creation and publishing may overlap | Creator and Publisher roles can be separated |
| Limited flexibility | Permissions can be combined as needed |
| Access based mainly on role | Access based on responsibility |
This gives enterprise teams greater control over how responsibilities are distributed.
10 Types of User Permissions in MarketBeam
MarketBeam’s permission architecture provides ten permission categories.
1. Content Creator
Content Creators prepare social media content and participate in the publishing workflow.
2. Publisher
Publishers control publishing and scheduling responsibilities.
3. Reviewer
Reviewers participate in internal content review and approval workflows.
4. Amplifier
Amplifiers participate in employee amplification workflows.
5. Influencer
Influencers receive access associated with influencer workflows.
6. User Management
This permission provides access to relevant user-management functionality.
7. Analytics
Analytics users can access social media analytics functionality.
8. Monitoring
This permission provides access to monitoring capabilities.
9. Audit
Audit permission provides access to relevant audit functionality.
10. Settings
Settings permission provides access to applicable platform settings.
An important part of this model is that permissions are evaluated per user and per team.
Therefore, the same person can have one permission combination on one team and a completely different combination on another.
How Team-Level User Permissions Work
Team-level permissions solve a common enterprise access-control problem.
Imagine a global organization with separate teams for corporate communications, the United States, Europe, product marketing, and employee advocacy.
A social media manager may need Publisher and Analytics permissions for the corporate team but only Analytics access for another regional team.
A single organization-wide role would make this difficult.
Team-level permission management provides more flexibility.
A simple way to understand the model is:
User + Team + Permission = Authorized Action
Instead of:
User = Same Access Everywhere
This approach is particularly useful for enterprises managing multiple regions, brands, departments, business units, or agencies.
Content Creator vs. Publisher Permissions
One of the most important applications of user permissions is separating content creation from final publishing.
Creating a social media post and deciding when it goes live are different responsibilities.
A Content Creator can prepare content, select the social channel, attach media, and suggest a publishing date.
However, that does not necessarily mean the creator should control final publication.
In MarketBeam’s workflow, the Content Creator can send the prepared post forward to a Publisher. The suggested date travels with the content as context, while the Publisher retains responsibility for final scheduling.
The Publisher can review the prepared post, adjust the schedule when necessary, and commit the final schedule.
Once the Publisher schedules the content, the creator cannot directly overwrite the scheduled post. It must first be unscheduled by the Publisher before returning to an editable state.
The responsibility boundary is clear:
Content Creator → prepares content
Publisher → controls final scheduling
This separation can help organizations reduce accidental changes and maintain clearer publishing authority.
What Is Permission Management?
Permission management is the process of assigning, reviewing, changing, and removing user access based on responsibilities.
For a social media team, permission management should answer questions such as:
- Who can create posts?
- Who can publish content?
- Who can review content?
- Who can manage users?
- Who can access analytics?
- Who can monitor conversations?
- Who can access audit functionality?
- Who can modify platform settings?
Good permission management makes these responsibilities explicit.
However, permission management should not be treated as a one-time configuration.
Employees change positions. Agencies complete projects. Team structures evolve. People cover for colleagues. New employees join.
As a result, permissions should be reviewed regularly.
User Permissions and Content Approval Workflows
User permissions become particularly important when social media content requires internal review.
Consider a workflow where a Content Creator prepares a post but another authorized user must review it.
In MarketBeam, a creator can submit content for internal review and assign it to a Reviewer.
The content author cannot review their own submission.
The assigned Reviewer can then inspect the content, add comments, approve it, or provide feedback requesting changes.
Therefore, the workflow can look like:
Create → Submit → Review → Revise → Approve → Schedule → Publish
User permissions determine who can perform each step.
Why Preventing Self-Approval Matters
Separation of duties is an important principle in controlled approval workflows.
If the person creating content can independently approve the same content, the review step provides less separation.
That is why MarketBeam prevents the content author from being assigned as the Reviewer of their own submission.
Importantly, this applies even when someone has multiple permissions.
For example, an employee may hold both Publisher and Reviewer permissions. If that person creates content requiring internal review, another eligible Reviewer can still review the submission.
Multiple permissions therefore provide operational flexibility without automatically eliminating review controls.
Can One User Have Multiple Permissions?
Yes.
Granular user permissions do not mean every employee must perform only one function.
Enterprise social media professionals frequently have multiple responsibilities.
For example, a senior social media manager could require:
- Publisher
- Reviewer
- Analytics
- User Management
Another employee might only require Content Creator and Analytics permissions.
The advantage is that these capabilities can be assigned intentionally instead of being automatically bundled into a broad administrator role.
How User Permissions Support Social Media Governance
Social media governance defines how an organization manages social media, who is responsible for specific actions, and what controls apply to those activities.
Three elements work together:
Policies define expectations.
Workflows define processes.
User permissions determine who can perform actions.
For example, an organization’s social media policy may state that only authorized social media managers can publish from corporate accounts.
The workflow can require Content Creators to send posts to Publishers.
User permissions can then restrict publishing responsibilities to users with Publisher access.
As a result, governance becomes more than a written policy. It becomes part of the operational workflow.
How User Permissions Reduce Social Media Risk
Internal access is an important part of social media risk management.
Organizations should consider scenarios such as:
- A creator accidentally publishes unfinished content
- A contractor receives unnecessary administrative access
- Someone changes settings outside their responsibility
- Content is published before internal review
- A former team member retains unnecessary privileges
- A user receives access to another team’s workflow
Granular permissions cannot eliminate every social media risk.
However, they can reduce unnecessary access and establish clearer boundaries between responsibilities.
This aligns with the security principle of least privilege.
Least privilege means users receive only the access necessary to perform their responsibilities.
For example, someone who only needs social media analytics should not automatically receive publishing or Settings permissions.
User Permissions and Social Media Compliance
User permissions can also support social media compliance by helping organizations establish controlled workflows.
This can be particularly relevant for regulated industries such as pharmaceuticals, life sciences, medical technology, healthcare, and financial services.
These organizations may require additional oversight before social media content is published.
For example, an organization could separate responsibilities between:
Content Creator → Reviewer → Publisher
The creator prepares the content.
The Reviewer evaluates it.
The Publisher controls final scheduling.
However, user permissions alone do not make an organization compliant with a specific regulation.
Compliance typically requires a broader combination of policies, internal procedures, training, review processes, technical controls, documentation, and ongoing oversight.
User permissions are one technical control within that larger governance framework.
Permissions, Workflows, and Notifications
Access control becomes more effective when it works together with workflows and notifications.
The relationship is simple:
Permissions determine who can act.
Workflows determine when they should act.
Notifications tell them when action is required.
For example, when a MarketBeam Content Creator sends a post forward for scheduling, eligible Publishers can receive a notification.
Similarly, when content enters internal review, the assigned Reviewer can receive a notification.
Once the review is completed, the submitter can receive an approval or feedback notification.
This creates a structured handoff between people rather than relying entirely on manual communication.
What Happens When a Reviewer Requests Changes?
Not every content review results in immediate approval.
A Reviewer may find something that needs to be changed.
In that situation, the Reviewer can provide feedback and request revisions.
The author can then review the feedback, modify the content, resolve the relevant reviewer comment, and resubmit the post.
The Reviewer receives the revised submission and can evaluate it again.
The process becomes:
Submission → Review → Changes Requested → Revision → Resubmission → Approval
This provides a structured content revision cycle.
Can a Reviewer Be Reassigned?
Enterprise workflows need flexibility because reviewers may become unavailable or responsibilities may change.
MarketBeam allows eligible pending review items to be reassigned.
However, several controls apply.
The review must still be pending. The replacement must be an active Reviewer on the same team. Additionally, the content author cannot become their own Reviewer.
When reassignment succeeds, the newly assigned Reviewer receives a notification.
This provides flexibility without removing the underlying review controls.
Best Practices for Managing User Permissions
Organizations implementing granular user permissions should follow several principles.
Follow the Principle of Least Privilege
Give each person only the capabilities necessary for their responsibilities.
Separate Content Creation and Publishing
Not every employee who creates content needs final publishing authority.
Prevent Self-Review
When independent internal review is required, authors should not approve their own submissions.
Use Team-Level Permissions
Employees may have different responsibilities across brands, regions, or business units.
Allow Multiple Permissions When Necessary
Some employees legitimately perform several functions. Permissions should be combined intentionally.
Review User Access Regularly
Responsibilities change, so access should be reviewed periodically.
Remove Unnecessary Permissions
Temporary access should not automatically become permanent.
Connect Permissions to Workflows
Permissions are most useful when they correspond directly to real operational responsibilities.
User Permissions for Regulated Industries
Permission management becomes especially valuable when social media operates within a regulated environment.
Pharmaceutical, biotech, MedTech, healthcare, and financial-services organizations may need stronger controls over who creates, reviews, approves, schedules, and administers social content.
Consider a pharmaceutical social media workflow.
A brand team creates the content.
An eligible Reviewer evaluates it according to the organization’s internal review process.
An authorized Publisher controls final scheduling.
The exact workflow will depend on the organization’s policies and applicable requirements.
However, the underlying access-control principle remains the same:
Access should match responsibility.
How MarketBeam Approaches User Permissions
MarketBeam’s updated permission architecture moves away from relying on a single broad Admin role for operational access.
Organizations can assign permissions across:
Content Creator, Publisher, Reviewer, Amplifier, Influencer, User Management, Analytics, Monitoring, Audit, and Settings.
More importantly, permissions are evaluated at the user and team level.
Therefore, one person could be a Content Creator on one team while having Publisher responsibilities on another.
Users can also hold multiple permissions when their responsibilities require them.
For example, someone can have both Publisher and Reviewer access while still being prevented from reviewing their own submitted content.
This creates a permission model designed around how enterprise social media teams divide responsibilities.
Frequently Asked Questions About User Permissions
What are user permissions?
User permissions determine which actions an individual is authorized to perform within a software platform. In social media management, permissions can control content creation, reviewing, publishing, analytics, monitoring, auditing, user management, and Settings access.
Why are user permissions important?
User permissions help organizations limit unnecessary access, establish clear responsibilities, control publishing authority, and strengthen social media governance.
What is permission management?
Permission management is the process of assigning, reviewing, changing, and removing user access according to organizational responsibilities.
What is least-privilege access?
Least privilege means giving users only the access required to perform their responsibilities instead of providing broad access by default.
Can one user have multiple permissions?
Yes. A granular permission system can combine capabilities when necessary. For example, a social media manager may require Publisher, Reviewer, and Analytics permissions.
Can users have different permissions across teams?
Yes. MarketBeam evaluates permissions per user and per team. Therefore, the same person can have different permission combinations across different teams.
Can a creator review their own social media post?
MarketBeam’s internal-review workflow prevents the content author from being assigned as the Reviewer of their own submission.
How do user permissions support social media compliance?
User permissions can support compliance processes by restricting access and helping organizations enforce defined responsibilities and approval workflows. However, permissions alone do not guarantee regulatory compliance.
What is the difference between a Content Creator and Publisher?
A Content Creator prepares content. A Publisher has responsibility for final scheduling within the MarketBeam creator-to-publisher workflow.
Build Better Social Media Governance With Granular User Permissions
Enterprise social media access should not simply answer:
“Who can log in?”
Organizations should also understand:
“What can each person do after they log in?”
Granular user permissions provide a more precise answer.
Content Creators can prepare posts. Reviewers can evaluate submissions. Publishers can control scheduling. Analytics users can access performance information. Administrative capabilities can be assigned only where they are required.
Team-level permissions provide even greater flexibility because the same employee can have different responsibilities across different teams.
For enterprises managing multiple brands, regions, employees, agencies, and regulated workflows, moving from broad administrative access toward granular permission management can create clearer responsibilities and stronger social media governance.